How to protect your Shopify store from app security flaws
What Shopify's own security guidance expects of apps, how to vet the apps you install, and how to read and act on a security advisory when one affects your store.
- Published
- 17 Oct 2026
- As of
- 17 Oct 2026
This guide is for merchants and Shopify developers who want to keep a store safe from app and theme vulnerabilities. It covers what Shopify expects of apps, what that means for your review process, and how to read an advisory when one affects you.
Why app security is your problem too
When you install an app, you hand it a set of keys to your store. According to Shopify's app authentication docs, apps call the GraphQL Admin API to read and write store data on behalf of merchants. That is real access to real data, and it runs with your store's authority, not the app developer's.
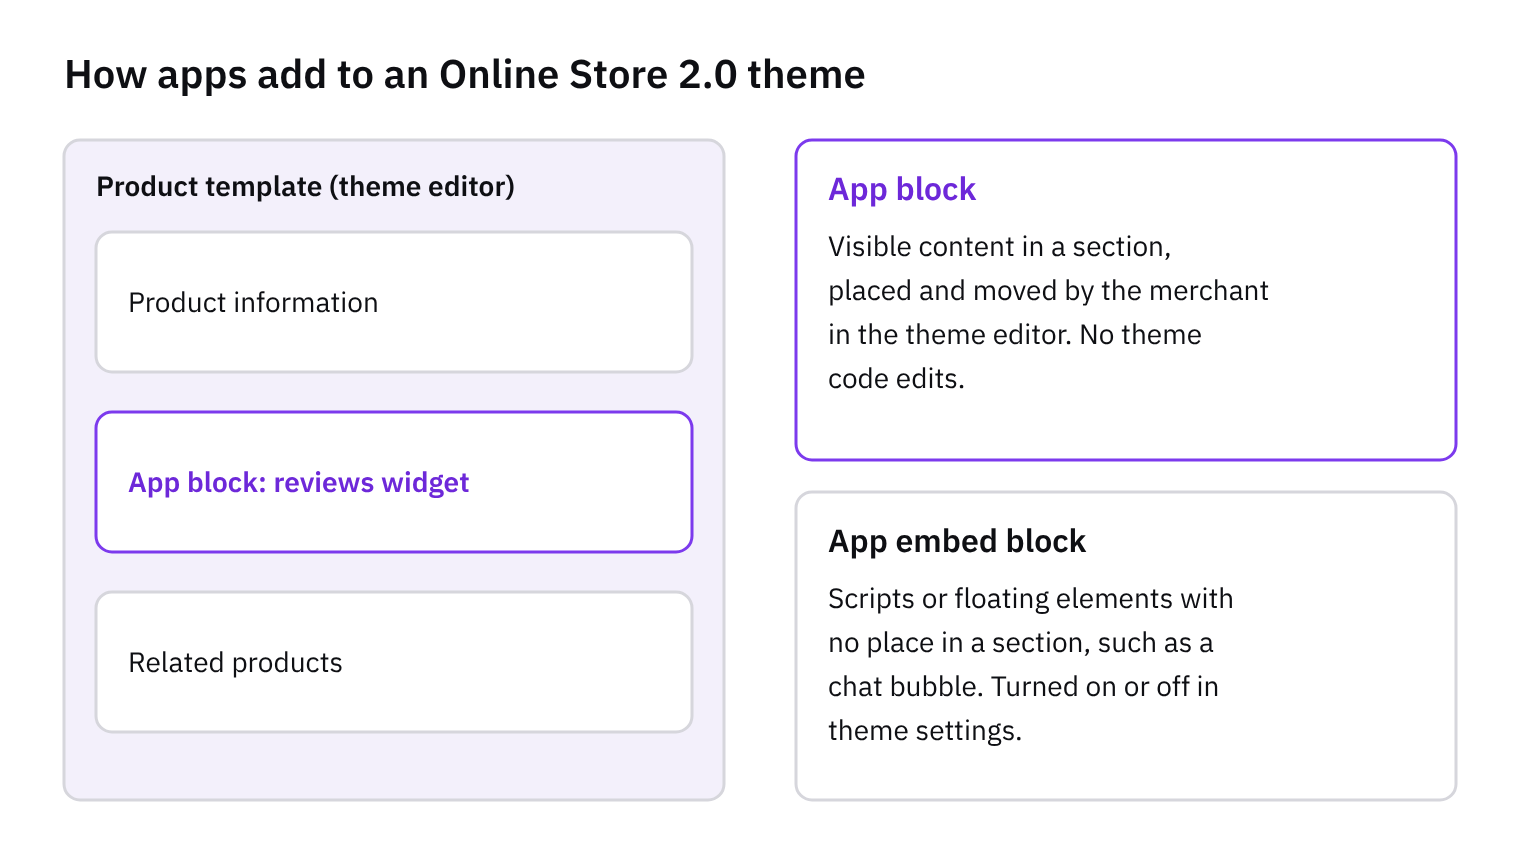
The keys are access tokens and scopes. Shopify's docs say the app sends its token in the X-Shopify-Access-Token header on every GraphQL Admin API request. So anyone who gets hold of that token can make the same requests the app can. The docs also note that any scope that writes a resource grants read access to it too. A write permission is never just a write permission.
This is why a weak app is a weak point for your store, even if your theme and settings are tidy. The risk follows the permissions, not the app's popularity or how small it looks.
Here is the practical tip. Before you install anything, read the scopes it asks for and ask whether each one matches what the app does. Developers should do the same for their own apps: the docs advise requesting the write scope only when the app needs both reading and writing. Fewer permissions means less exposed if something goes wrong. Merchants can also review installed apps now and then and remove any they no longer use.
What Shopify checks before an app is listed
Before an app is listed, Shopify's app review checks five security requirements, according to its app security guide. They are protection against common web vulnerabilities, encryption in transit, closed network service ports, secure token generation, and careful handling of shortened URLs. It is a useful checklist for judging any app, listed or not.
The first requirement is broad. Shopify expects third-party apps to be protected against common web security vulnerabilities, "including but not limited to, The OWASP Top 10". That is a well-known list of the most common web app risks. Encryption in transit means data is scrambled between the browser, the app and Shopify, so it can't be read on the way. Closed ports are about not leaving services open to the internet that don't need to be. During review, Shopify uses the Nmap security tool to identify open ports.
The last two are about tokens and links. Tokens used for authentication must be randomly generated with 128 bits of entropy, which is a measure of how hard they are to guess. The guide allows 64 bits in some cases where token length is a concern. Publicly accessible tokens, such as URL parameters, must expire within no longer than seven days. Shortened URLs are a risk because the guide says URL shortening is vulnerable to brute-force attacks, so they shouldn't be used for URLs that might hold confidential information, such as checkout or order URLs.
Here is the practical tip. Ask a vendor how they meet each of these five points, in plain terms. Good questions: how do they test for OWASP Top 10 issues, how long do their link tokens last, and do they ever put order or checkout links through a shortener? A vendor who has been through review should answer quickly. If you're a developer, use the same list as a self-check on your own custom apps before you ship.
Tokens, scopes and what to look for in your own builds
If you build or maintain an app, start with how it talks to the store. Shopify's app authentication docs say the app sends the access token in the X-Shopify-Access-Token header on every GraphQL Admin API request. So treat that token like a password. Keep it server-side, keep it out of logs and error reports, and never ship it to the browser. A leaked token lets someone act with whatever scopes the app holds.
That brings us to scopes. The same authentication docs say any scope that writes a resource also grants read access to it, so request the write scope only when your app needs both. In practice, that means auditing your scope list at each release. If a feature was dropped, drop its scope too. A smaller scope list limits what a stolen token can reach, and it is also easier to explain to merchants at install.
Shopify's app security guide sets out what app review checks for tokens. Tokens used for authentication must be randomly generated with 128 bits of entropy, and 64 bits is allowed in some cases where token length is a concern. Use your platform's cryptographically secure random generator rather than anything built from timestamps or counters. Publicly accessible tokens, such as those in URL parameters, must expire within no longer than seven days. We'd go shorter where the flow allows, and make them single-use, because a link that lives in an inbox or browser history is easy to pass around.
The same guide warns that URL shortening is vulnerable to brute-force attacks. Don't use shortened URLs for anything that might hold confidential information, such as checkout or order links. If you send customers a link to an order, give them the full URL with a properly random, expiring token. It's a little longer, but it's much harder to guess.
Reading an advisory and responding
Start with three questions when you open an advisory in the National Vulnerability Database or the GitHub Advisory Database. What was affected: the app, theme or library, named exactly. Which versions: advisories usually give a range, so check yours against it rather than assuming. And was it fixed: look for a patched version or a note that no fix exists yet. If the entry doesn't say, treat it as unfixed and ask the vendor. Read the description for what the flaw allows too, because that tells you how urgent it is for your store.
Then work through the store. Keep an inventory of every installed app, theme and library, with versions and who owns each one. Compare it against the advisories you care about. If a fix exists, update. If it doesn't, or the app is abandoned, remove it. Next, review scopes. Shopify's app authentication docs say any scope that writes a resource also grants read access to it, and every request carries the access token in the X-Shopify-Access-Token header. So an app with broad scopes can do more damage if something goes wrong. Ask whether each app still needs what it holds.
Developers can use Shopify's app security docs as a checklist for custom and partner apps. The review there checks protection against common web vulnerabilities such as the OWASP Top 10, encryption in transit, closed network service ports, secure token generation, and careful handling of shortened URLs. It also says publicly accessible tokens, such as URL parameters, must expire within no longer than seven days. When an advisory describes a weakness, check your own code against that list.
Get the weekly digest
One email every Monday: the week’s new guides and articles, plus the Shopify deadlines coming up and what’s been announced. Free, and you can unsubscribe in one click.
Sources
- About app authentication · shopify.dev · accessed 16 Oct 2026
- About app security · shopify.dev · accessed 16 Oct 2026
AI-assisted, reviewed by Scott. Every claim is checked against the sources above.